When Dino stops, it tells you whose problem it is
September 29, 2026
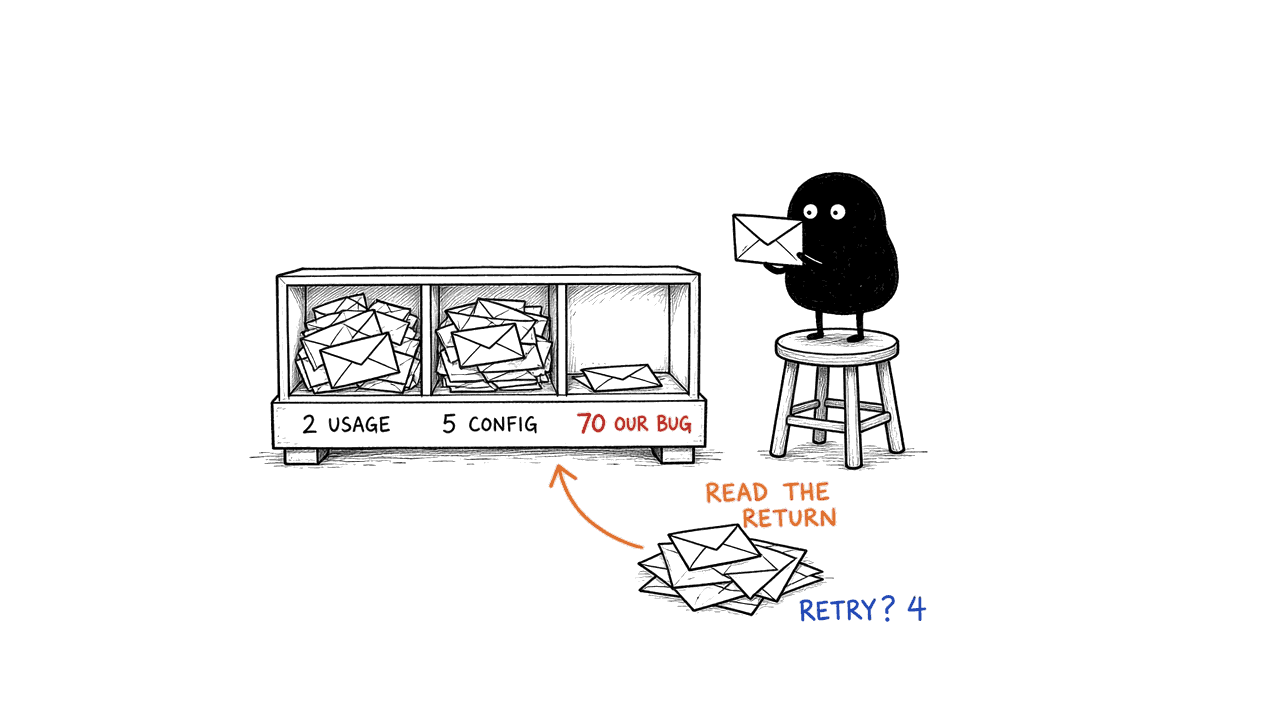
A mistake in your command or config now exits 2 or 5 with what to fix, never "Dino crashed". Tenant auth reaches every probe, a bad credential stops the scan instead of becoming a finding, and Dino reports fewer false findings.
Exit codes you can script against
Dino 1.2.1 is the first release of the 1.2 line. (1.2.0 was never published: its release stopped at a pre-release check before anything shipped.)
When a Dino run stops, the exit code now says whose problem it is:
- 2 means the command itself was wrong: a missing flag, or a value Dino can't use.
- 5 means your configuration or credentials need attention.
- 4 means your API or an upstream service couldn't be reached, so a retry may work.
- 70 is reserved for a genuine bug in Dino.
Before, many ordinary mistakes (a malformed endpoint, a broken operations file, an empty tool selection) ended as 70, "Dino crashed". Every failure now declares its outcome, and the message on screen and the JSON error on stderr always say the same thing.
If your CI treats any non-zero exit the same way, nothing changes for you. If you matched on 70, look for 2 and 5 instead.
Tenant authentication you can rely on
- The
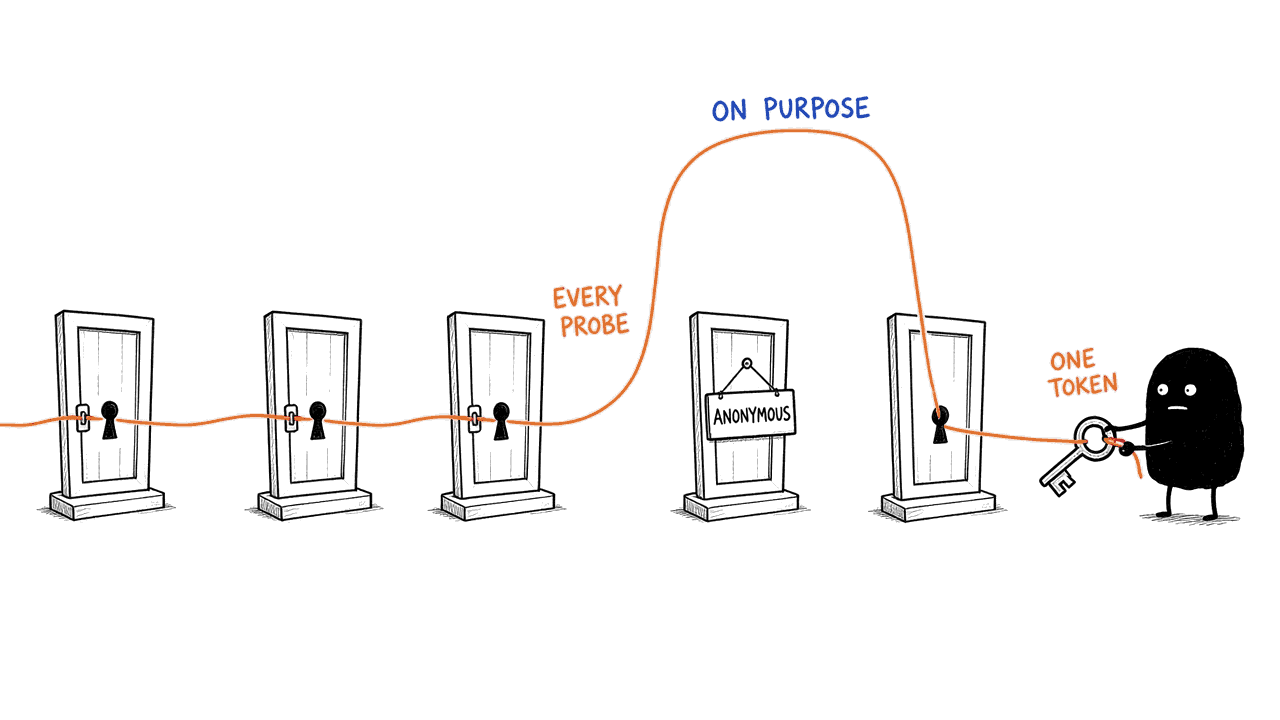
jwtadapter signs its own token. Before, it sent an empty request to your API and never authenticated. - Input fuzzing, response validation and rate-limit probes on GraphQL now carry your tenant's token. The one probe that must be anonymous is marked anonymous on purpose.
- A rejected or unreachable OAuth2 credential stops the scan: exit 5 when the provider rejects it, exit 4 when the provider is down. It no longer shows up as a finding against your API.
auth.enabled: truewith a tenant that has no auth adapter is refused before any request, with exit 5.
Fewer false findings
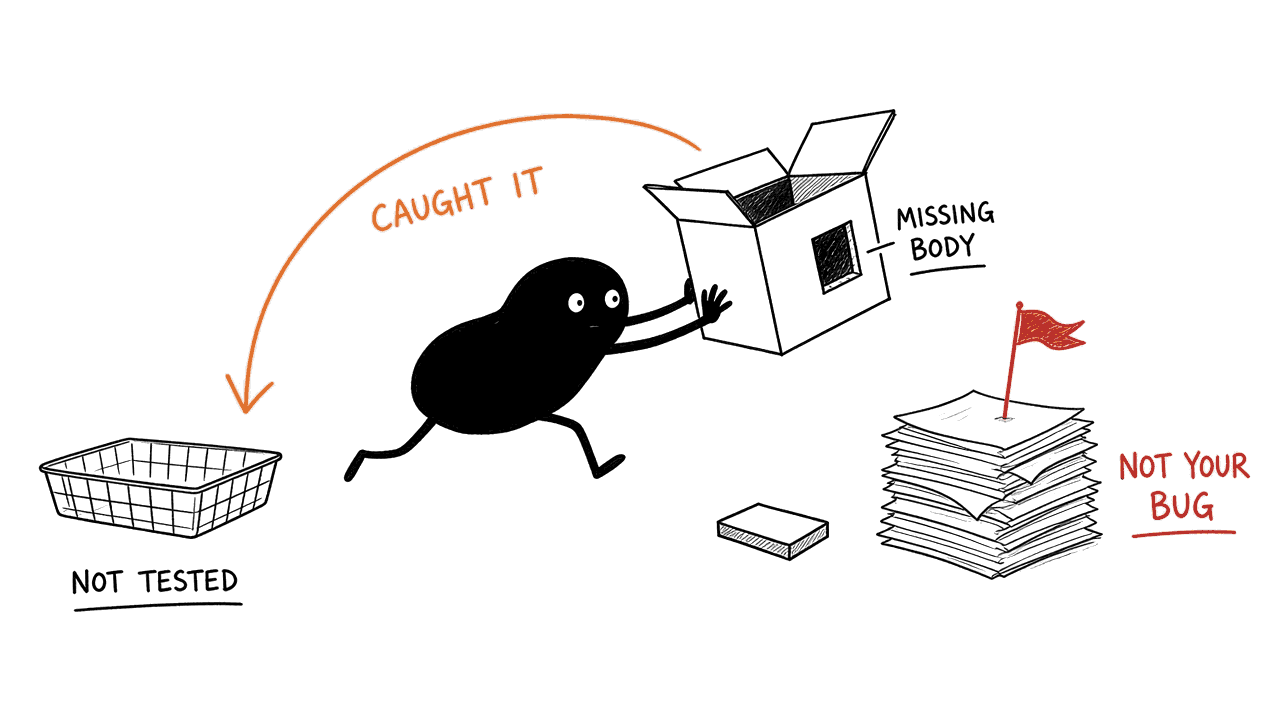
Dino no longer reports a finding from a request it couldn't send correctly. When an operation needs a query parameter or a request body Dino can't supply, the error-code validator, rate-limit check and response validator report it as not tested, instead of blaming your API for rejecting an incomplete request.
A leak pattern also no longer matches across two unrelated error messages.
Also in 1.2.1
- A file named in your configuration can't be read through a symlink that points outside its directory.
dino verify,dino whoamianddino runner registerno longer mark a failed request as retryable when retrying can't help.dino schemasays where--format jsonoutput goes: the result on stdout, errors on stderr.
Update with brew upgrade dino, npm install -g @dino-hq/cli@latest, or by running the installer again.